Critical Infrastructure. Noncritical Budget.
A small IT budget does not imply a small consequence of failure.
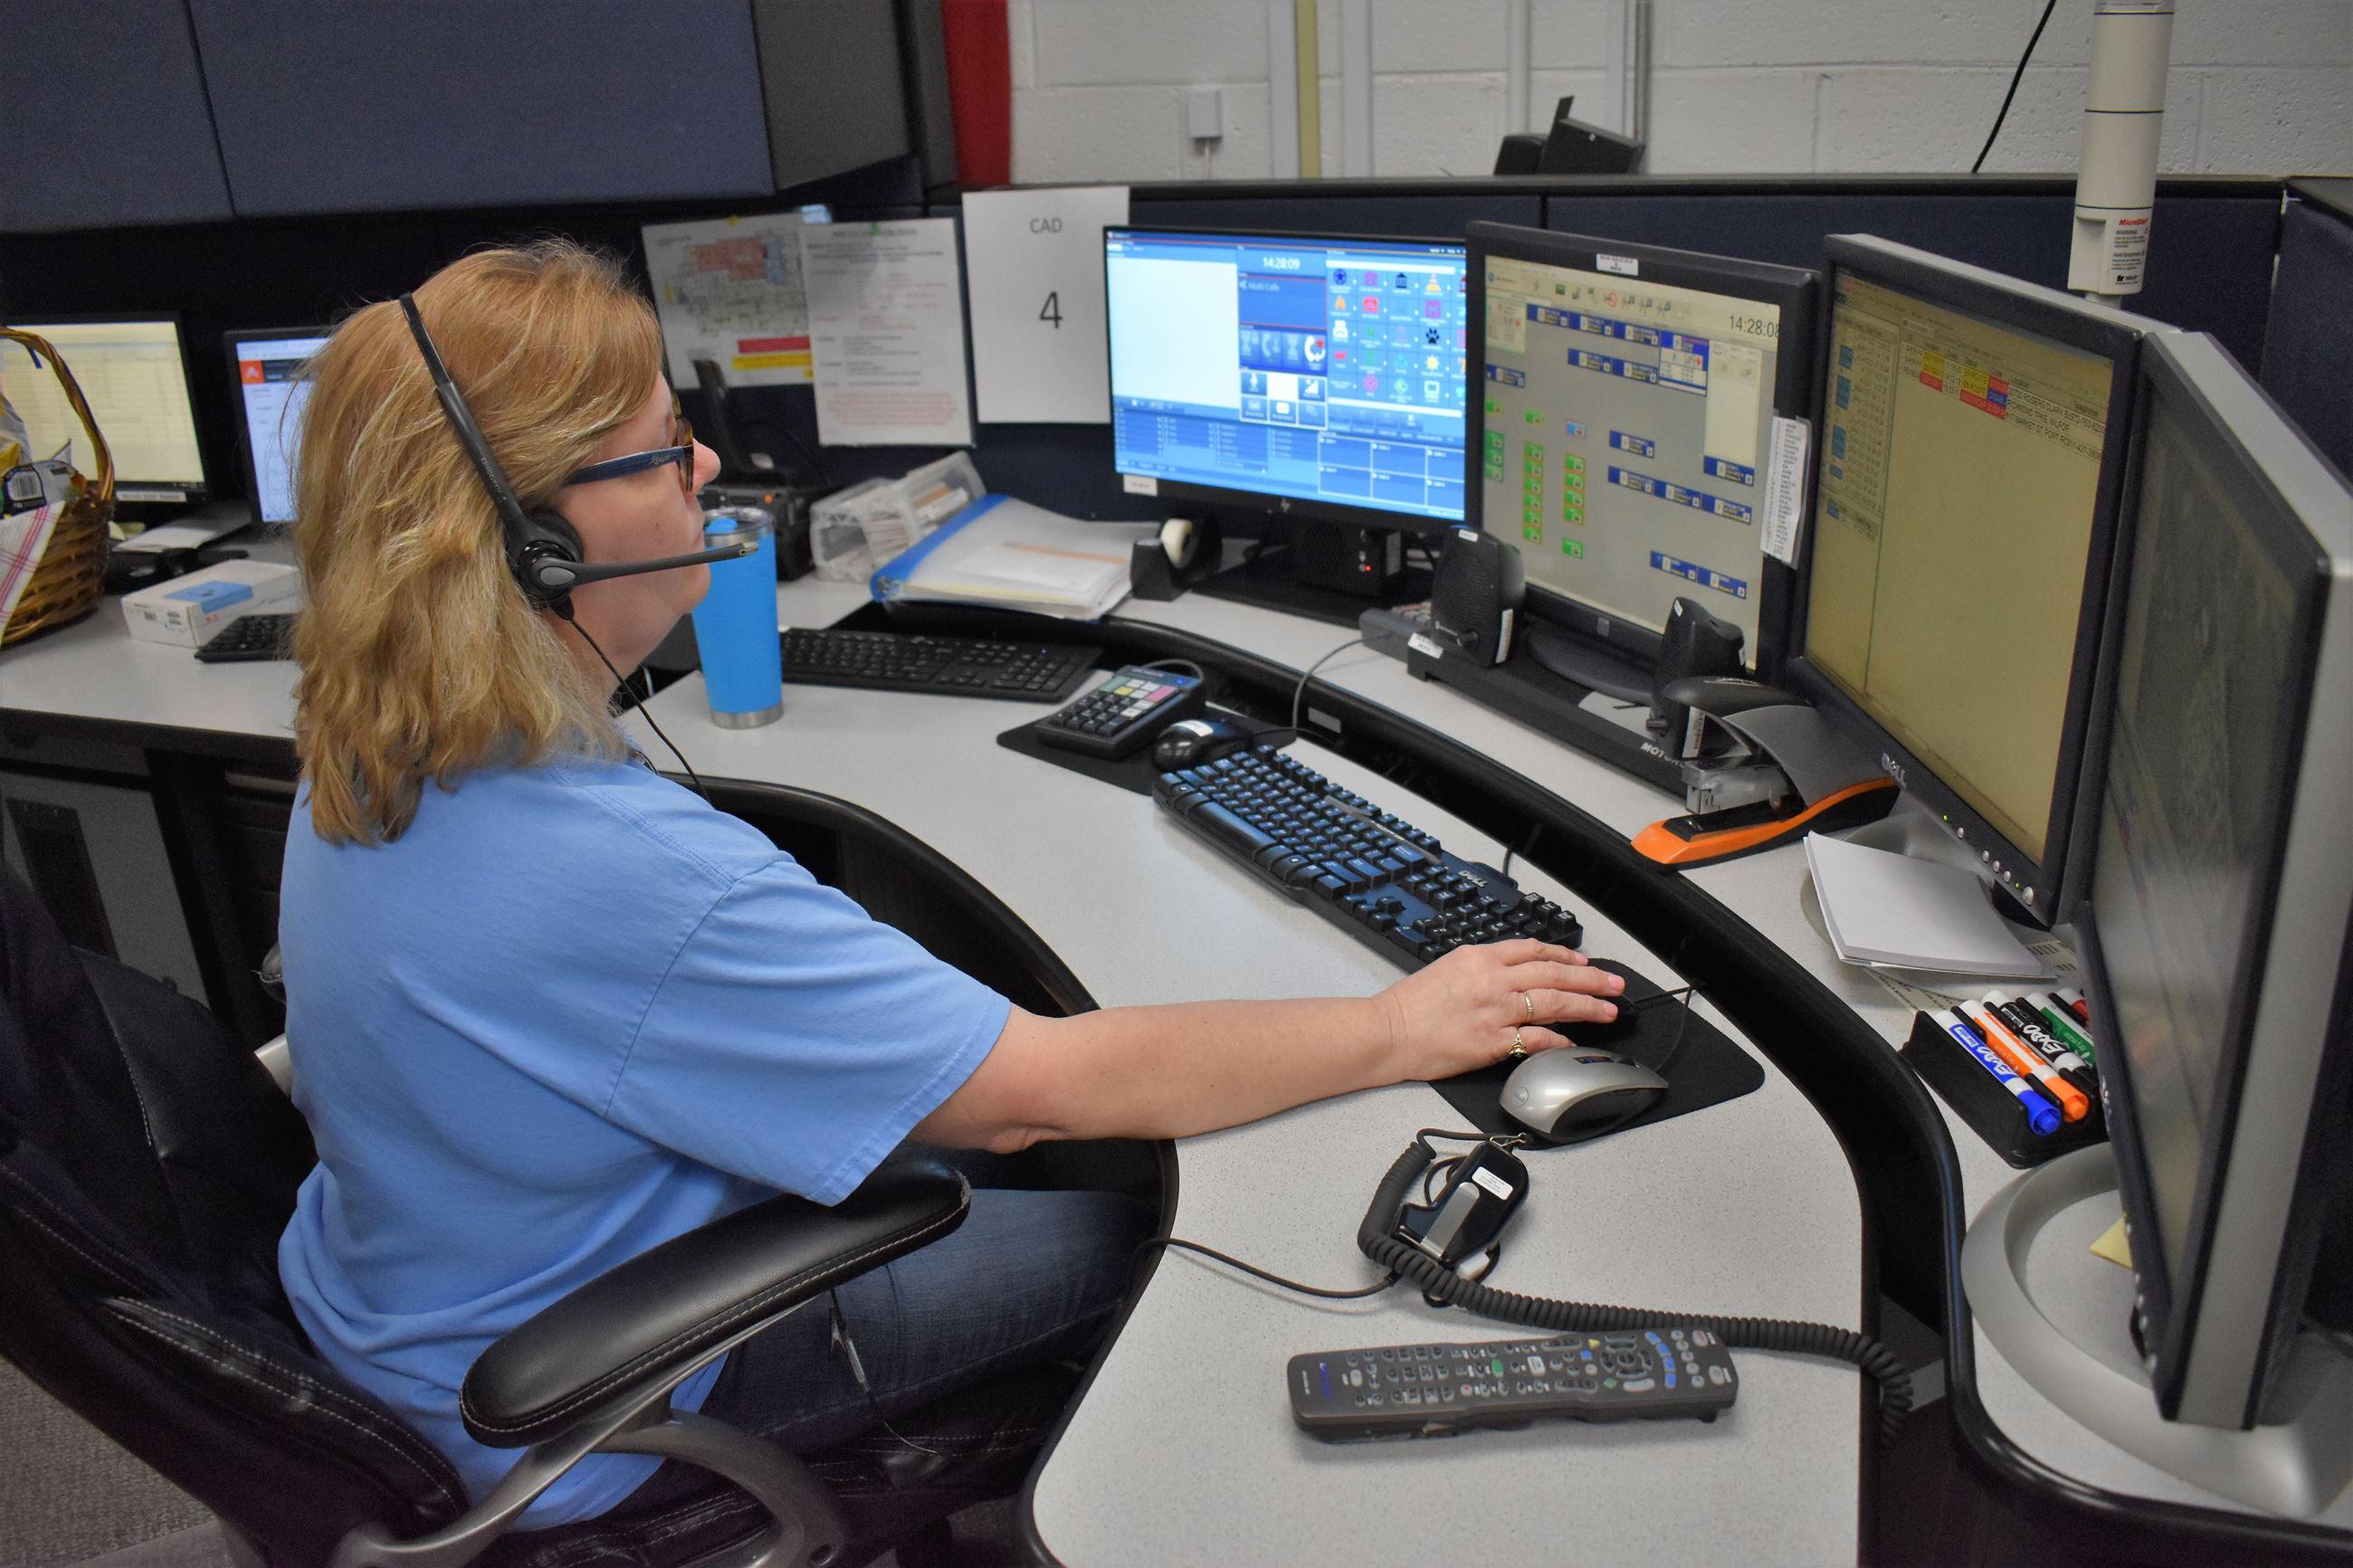
In emergency response, an underfunded municipal system can become the linchpin of a much larger regional operation. The agencies relying on that network may command substantial resources. The local team maintaining it may have very few.
Its criticality is determined by who depends on it. Its funding is determined by other factors.
And buying a security product is only the down payment.
Someone has to configure it, maintain it, review its findings, investigate alerts, and decide when to intervene. For a small team, a tool can be affordable to purchase and expensive to operate.
Now put that team in the middle of an emergency.
Demand spikes. Staff are occupied. Decisions become urgent. The consequences of an interruption grow.
Who has time to read the alert then?
Monitoring and incident response remain necessary. But when the same small team supports operations and security, every investigation draws on capacity the emergency response also needs.
That should change what we ask of cybersecurity:
- Can it interrupt reconnaissance and constrain lateral movement before essential services are disrupted?
- Can it enforce boundaries without waiting on an analyst?
- Can a small team afford to run it?
This is why we built Ridgeback. Phantom resources occupy otherwise unused network address space. Contact with those resources can trigger immediate, policy-based containment of the source, constraining further discovery and lateral movement without requiring an analyst to investigate first or an agent on every protected device.
Affordability has to include the people and attention required to keep the protection working.
The defense must still work when everyone is busy doing the job the network exists to support.